ISO 27001 Lead Auditor Training
As a Lead Auditor you assess whether an Information Security Management System really works. In this programme you learn to plan, conduct, report on and lead ISO 27001 audits, including first-, second- and third-party audits, and you finish with a practical audit simulation.
Who is the ISO 27001 Lead Auditor training for?
- Internal auditors
- (Aspiring) external auditors
- Information Security Officers
- Compliance and risk professionals
- Consultants
What you'll learn
Audit Foundations
- Audit principles
- ISO 27001 requirements
- Auditor responsibilities
- Audit planning and the audit programme
Audit Preparation
- Audit scope, objectives and criteria
- Audit plans
- Evidence requirements
- Preparing audit questions
Conducting the Audit
- Interview techniques
- Gathering objective evidence and sampling
- Assessing controls
- Identifying findings and non-conformities
Reporting
- Writing audit findings
- Audit reports
- Corrective actions and follow-up audits
- Closing findings
Leading the Audit
- Leading an audit team
- Managing the audit process
- First-, second- and third-party audits
- Audit scenarios and a practical audit simulation
Assessment
- Practical audit exercise
- Final assessment
- Feedback and completion
After the training
After completing the ISO 27001 Lead Auditor training you can:
- apply audit principles to ISO 27001
- set up an audit programme and audit plan
- define audit scope, objectives and criteria
- prepare effective audit questions
- conduct interviews and gather objective evidence
- assess controls and identify non-conformities
- write clear audit findings and reports
- follow up corrective actions and close findings
- lead an audit team through first-, second- and third-party audits
You also receive a certificate of completion and keep access to your facilitator for questions while you put it into practice.
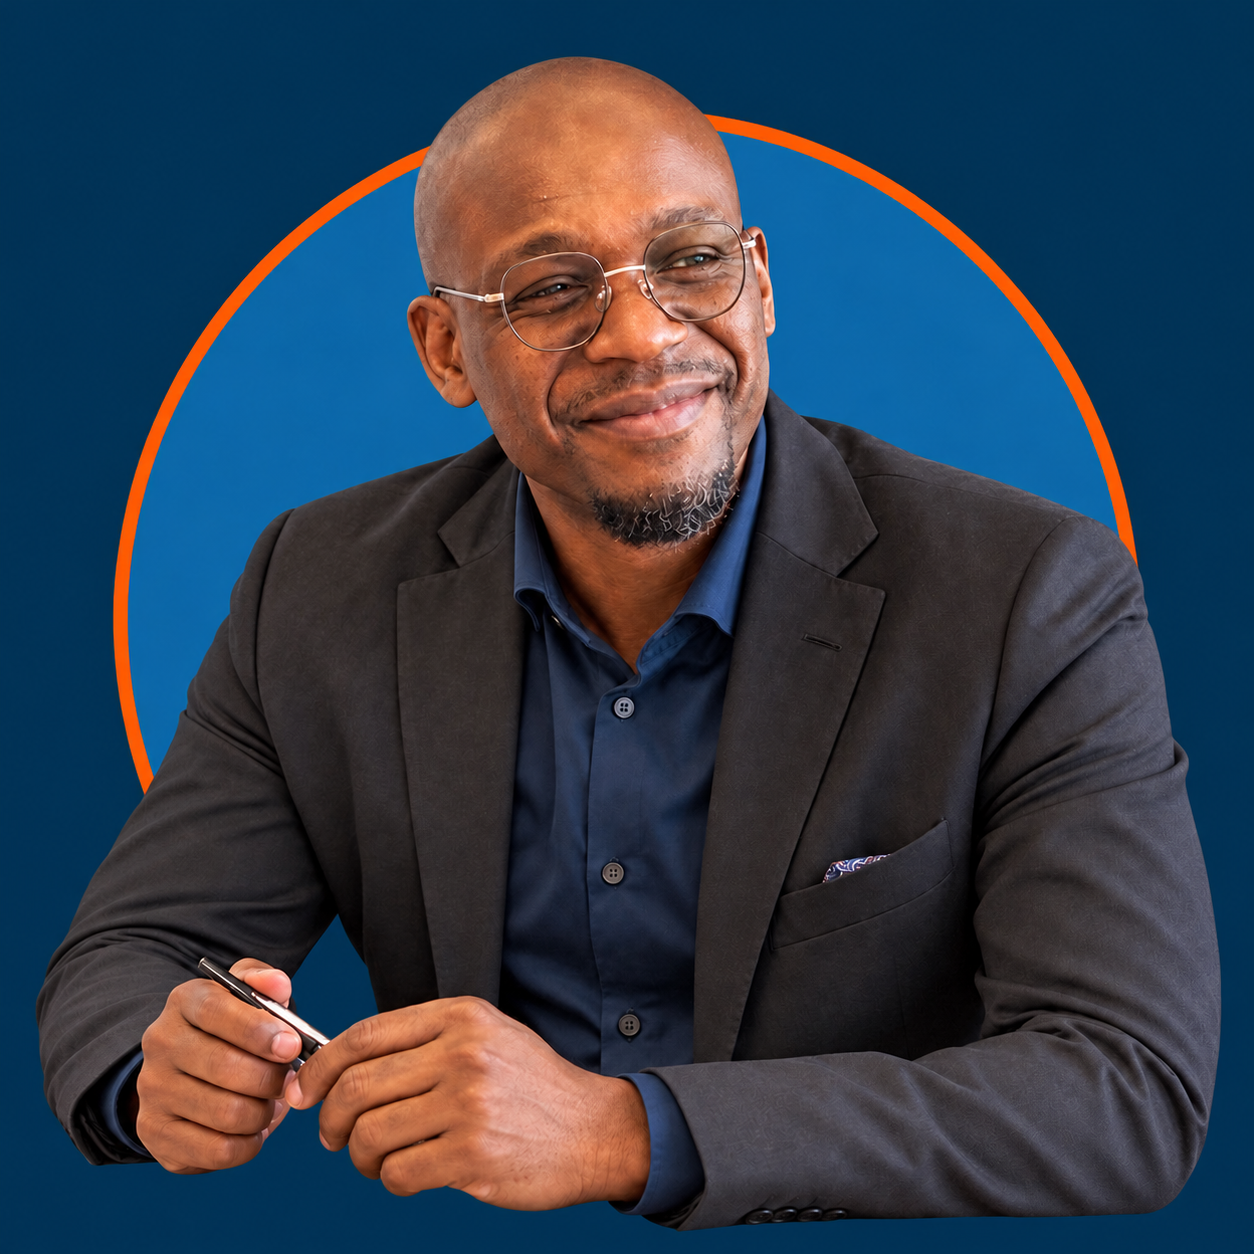
Bernard Chadenga
Head of Cyber Consulting · Cybersecurity, risk & ISO training specialist
Bernard Munyaradzi Chadenga is a subject matter expert and experienced trainer with over 20 years in cybersecurity, risk management and digital transformation across Southern Africa. He is first and foremost an educator. For years he has designed and delivered masterclasses and professional development programmes, and has mentored emerging talent, several of whom are now CISOs.
At the ISO Specialist Academy he brings that practical, boardroom-tested experience to ISO training. He shows learners how management system standards such as ISO/IEC 27001 work in practice, connecting governance, information security, enterprise risk and business strategy so the standards become workable tools rather than paperwork. Bernard has advised C-suite leaders and boards as a vCISO.
His training is known for making complex topics clear, and he teaches with energy and authority, giving delegates the knowledge and confidence to build, implement and sustain resilient, compliant organisations.
Enrol for the ISO 27001 Lead Auditor training
All sessions are live and virtual, and new dates are scheduled regularly. Enrol now or ask about the next available date and private sessions for your team.
- Price
- R20,684
- Time
- 5 days
- Structure
- 5–6 weeks / 25–30 hours
- Format
- Virtual programme + audit simulation
Experiences of participants
The strength of our training is the combination of practice, interaction and direct applicability. Participants value that:
- the training is directly applicable in their work
- the realistic cases help them really understand the standard
- the guidance is personal and involved
- they feel more confident in their role
- they stand stronger towards management and colleagues
Which training is right for me?
Want everyone to work securely? Start with Cyber Awareness for all staff and the ISO 27001 Introduction for the people involved in your ISMS.
Responsible for setting up the ISMS? ISO 27001 Implementation takes you from scope and risk assessment to controls and internal audit in two weeks.
Leading the project or auditing it? Choose Lead Implementer to run the full certification project, or Lead Auditor to plan and lead ISO 27001 audits.
Not sure which training suits your role or learning goals? Request a quote or book a call with Sam, our training coordinator.
Frequently asked questions
What is the ISO 27001 Lead Auditor Training?
As a Lead Auditor you assess whether an Information Security Management System really works. In this programme you learn to plan, conduct, report on and lead ISO 27001 audits, including first-, second- and third-party audits, and you finish with a practical audit simulation.
Who is the ISO 27001 Lead Auditor training intended for?
This training is intended for internal auditors, (Aspiring) external auditors, information Security Officers, compliance and risk professionals and consultants.
What will I learn during the ISO 27001 Lead Auditor training?
You will learn to apply audit principles to ISO 27001, set up an audit programme and audit plan, define audit scope, objectives and criteria, prepare effective audit questions and more. See the programme above for the full outline.
Is this training suitable without an IT background?
Yes. The focus is on management, processes and organisation. Technical depth is limited and an IT background is not required.
Do I need prior knowledge to take part?
Knowledge of ISO 27001 is recommended, for example through our ISO 27001 Introduction or Implementation training.
Can we bring our own cases?
Yes. Wherever possible we work with practical situations from your own organisation, so you can apply what you learn straight away.
Can we book a private session for our team?
Yes. We can run a private virtual session for your team and tailor the examples to your organisation. Contact us to discuss the options.
What will I learn about Annex A?
You learn how Annex A is structured, how to select the controls that are relevant to your organisation and how to justify and document them in the Statement of Applicability (SoA).
Can I conduct audits myself after this training?
Yes. You learn to plan, conduct, report on and lead ISO 27001 audits, and you practise this in a realistic audit simulation.
Will I receive a certificate after the training?
Yes. After completing the training you receive a certificate of completion from ISO Specialist Academy.
How does this training help my organisation achieve ISO 27001 certification?
You learn what auditors look for and how to make the requirements work in practice, which helps your organisation prepare for the external certification audit with confidence.
What makes this training practical?
Your trainer, Bernard Chadenga, brings over 20 years of experience in cybersecurity, risk management and digital transformation, including advising boards as a vCISO. We combine knowledge of the standard with real examples, interactive exercises and templates you can use immediately.
Is the training delivered online?
Yes. For now, all our training is delivered virtually in live online sessions, so you can take part from anywhere without travelling.
We are ISO Specialist Academy
We believe training only has value if you can apply it the very next day. That's why you won't get dry theory from us, but practice-oriented training you can put to work in your organisation immediately.
Our trainers are consultants who guide organisations every day in quality, health and safety, environment and information security. They know what businesses face and translate complex standards into clear, practical steps.
Whether you need to understand a standard, run an internal audit or lead an implementation, our courses give you the knowledge and confidence to do it yourself, with personal attention and room for your questions throughout.
Get certification done.
Get to know us
Personal advice?
Have a question or want a free quote? Fill in the form and we'll contact you within 1 business day.